
Access Controls for Public Companies
Adaptive helps public companies enforce and prove the IT general controls behind SOX compliance and SEC cybersecurity disclosure requirements.
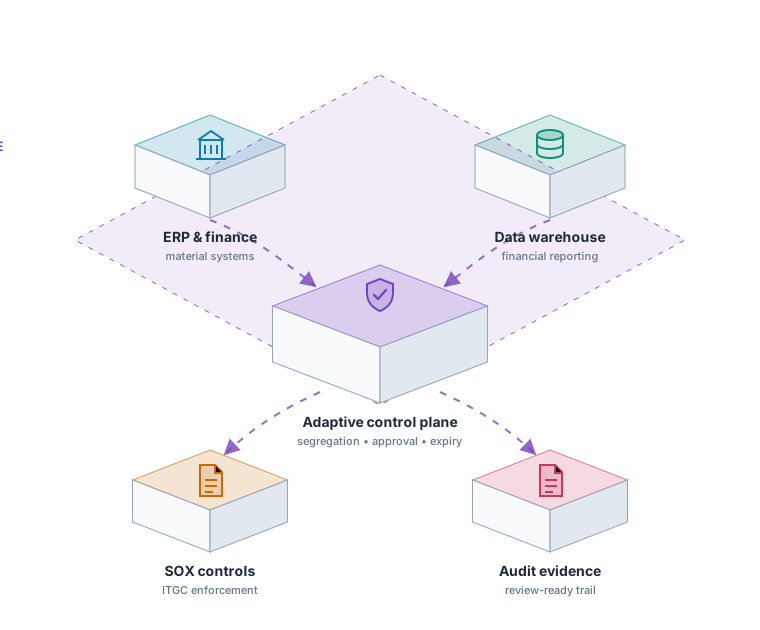
Public companies must show that access to financially significant systems is controlled, reviewed and logged, and they must disclose material cybersecurity incidents on tight timelines.
SOX audits test who can access the databases and systems that feed financial reporting, whether that access is reviewed, and whether changes are traceable. Manual access reviews, spreadsheets of approvals and screenshots of logs are slow and error-prone. Under the SEC cybersecurity rules, boards and management also need clear visibility into access risk so they can assess materiality quickly when an incident happens.
Continuous, provable access controls for SOX and SEC
Adaptive enforces just-in-time, approval-based access to financially significant systems and records every query and command in immutable audit logs. Periodic access reviews, segregation of duties and change traceability are built in, so ITGC evidence is available on demand. When an incident occurs, complete session and query history helps security and legal teams quickly scope impact and support disclosure decisions.
How Adaptive helps
ITGC Evidence on Demand
Generate access review, approval and activity reports for SOX auditors without manual evidence gathering.
Segregation of Duties
Enforce approval workflows and time-bound access so no single user holds standing privileged access to financial systems.
Faster Incident Scoping
Use complete session recordings and query logs to determine what was accessed during an incident, supporting timely materiality assessment and disclosure.
 |
 SOC2 Type II

