
Zero Trust Network Access
Inspired by Google's BeyondCorp architecture — every request is verified on identity and context, so you can securely share exactly the infrastructure resources and applications people need, across public and private subnets.
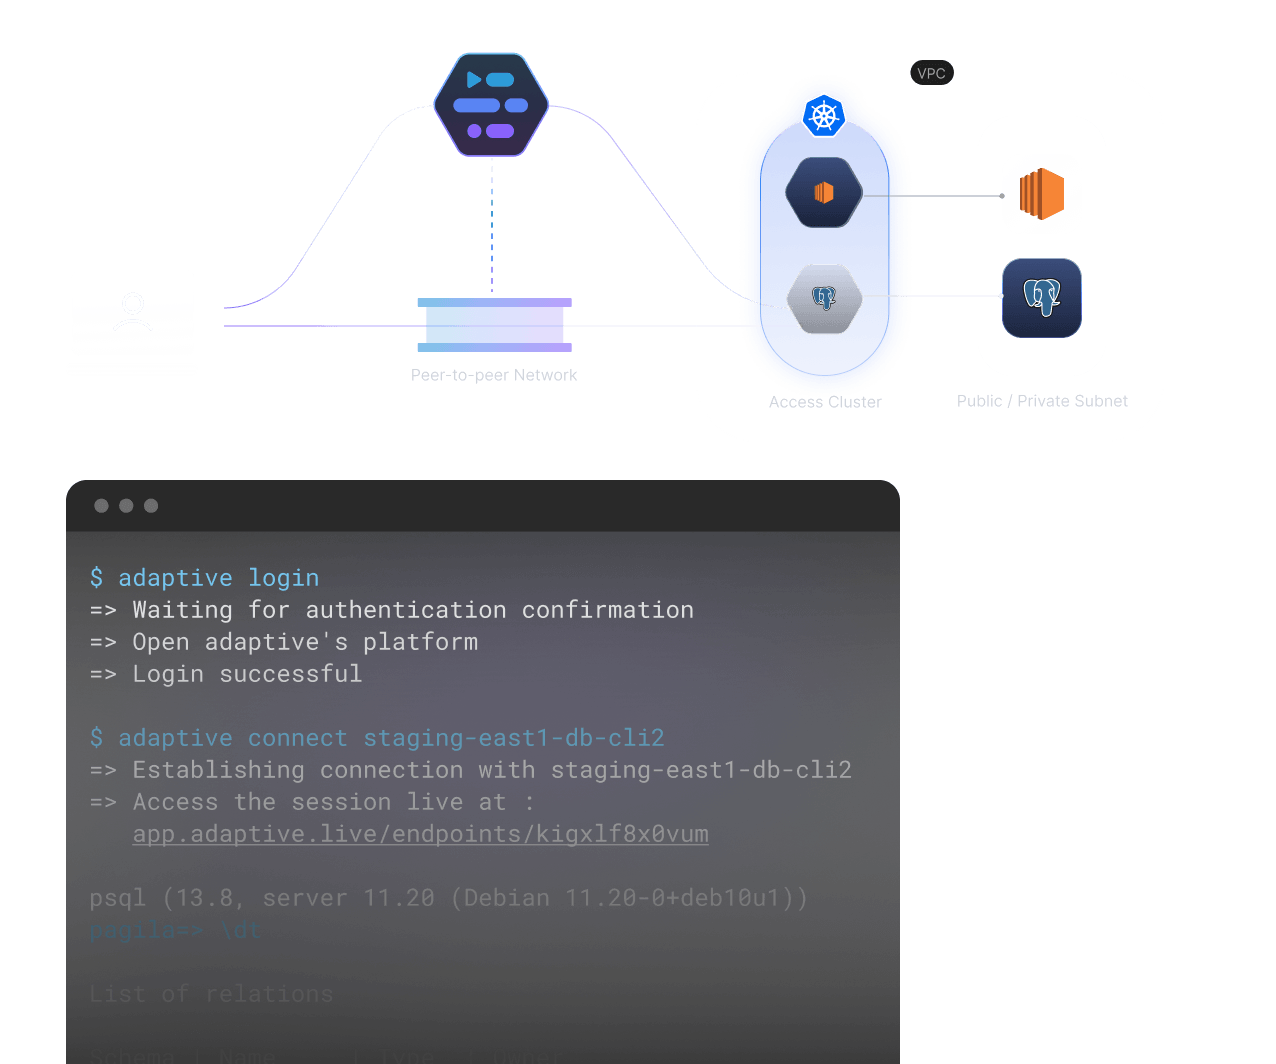
Traditional VPNs were designed to protect on-prem infrastructure resources. They are overly permissive and lack traceability. Modern infrastructure is on the cloud, ephemeral and collaborative and hence needs a solution that brokers access to specific resources. The Zero Trust Network Access model bridges this gap by providing fine-grained, identity-verified access specifically designed for modern, cloud-centric environments.
80%
Organizations face difficulties while implementing ZTNA
$1M
Data breaches in organizations without ZTNA could cost an additional $1 million


A ZTNA model that's easy to set up and scales with your organization
Adaptive’s container-based architecture allows organizations to deploy a zero-trust solution at scale without needing to make architectural, hardware, or software changes. The platform creates ephemeral secure tunnels to connect with infrastructure resources in any network across different VPCs, improving the organization’s security posture and increasing granular traceability.
Split Tunnelled Access
Create point-to-point secure tunnels on the fly - only establishing connections to the resources that are needed. Achieve resource-level network isolation natively without needing network reconfiguration.
Zero Knowledge Access Management
Ensure that accessors never see any key or credential while accessing any infrastructure resource or have any knowledge of the network that the resource resides in.
SSO and Multi-Factor Authentication
Enhance security by enabling multi-factor authentication on all infrastructure resources, protecting against unauthorized access and potential security threats.
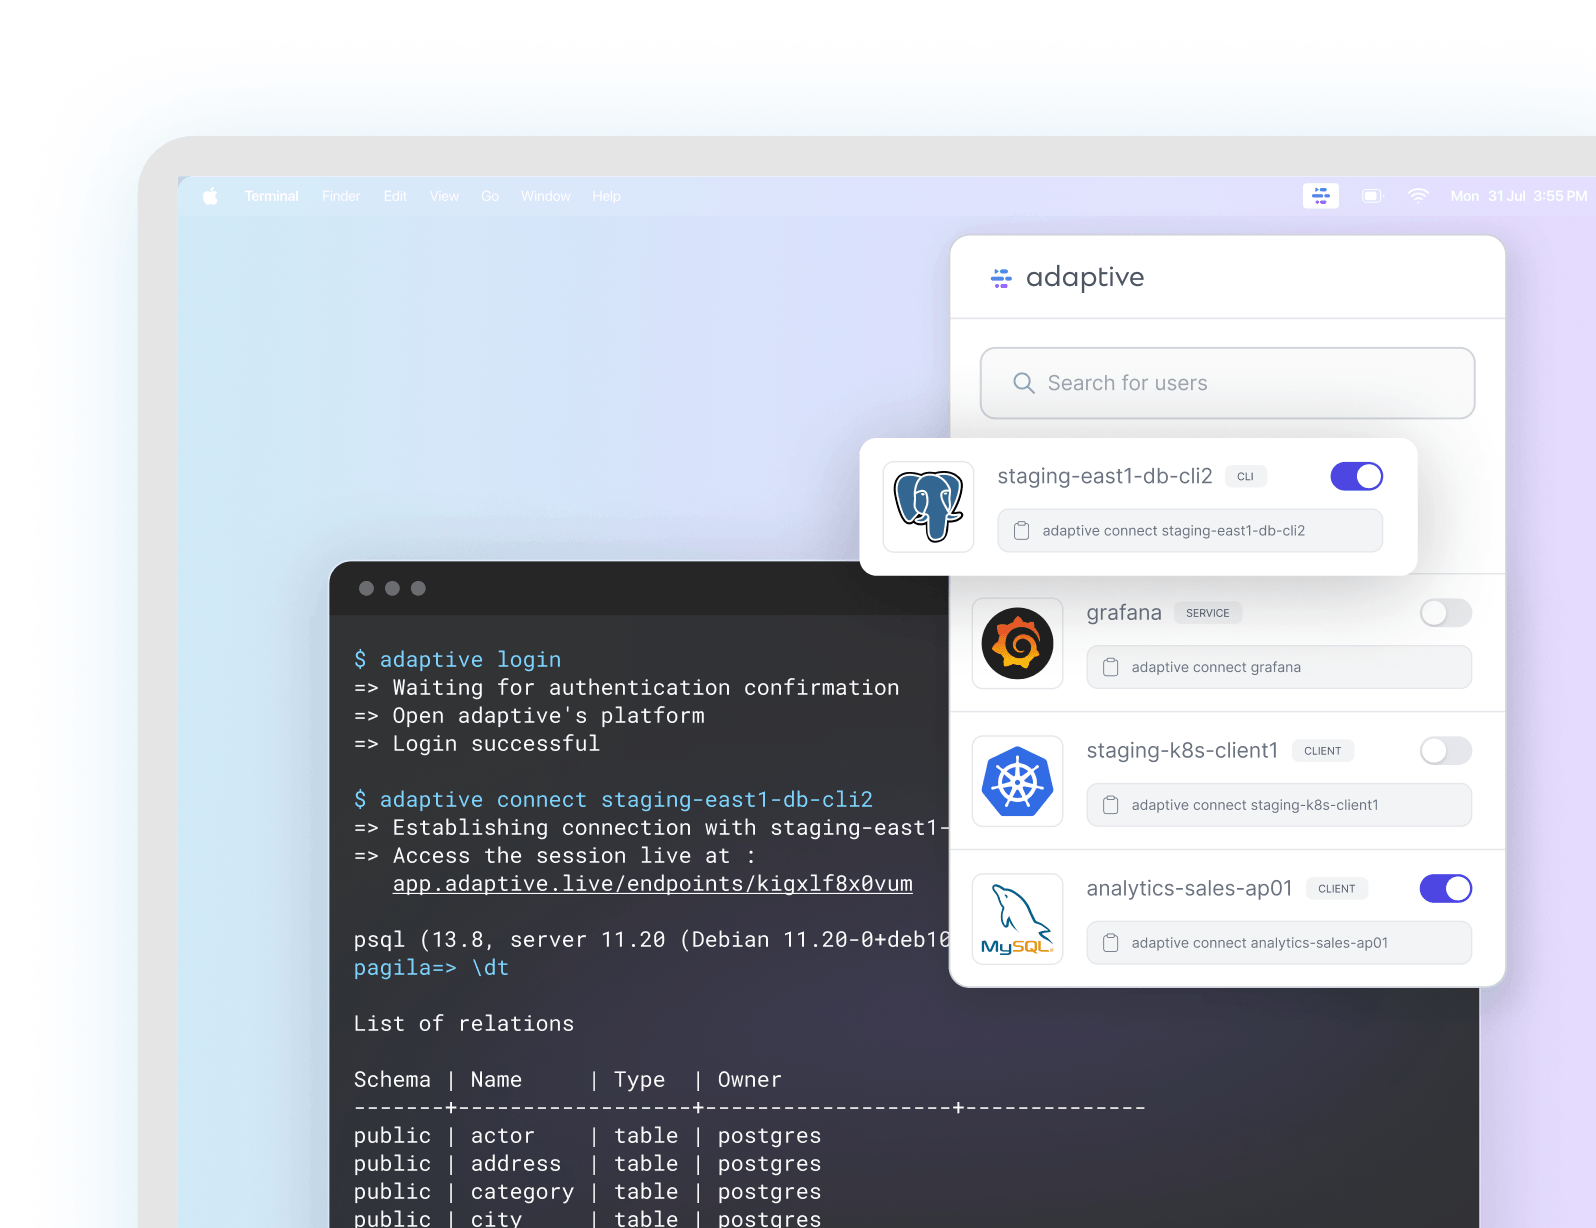
Zero Trust Network Access

No Network Changes Required

Cloud or On-Premises Deployment

Enterprise-Grade Security
Identity. Access. Data. Privileges. Governance.
 |
 SOC2 Type II
Access & Privileges
Data & Governance


© 2026 Adaptive Automation Technologies, Inc.